Elasticsearch
Connect Aiden with your Elasticsearch service to get intelligent assistance with real-time search, analysis, and visualization of your data. Once enabled, Aiden can help you fetch targeted logs, perform log analytics, and troubleshoot the root cause through natural conversations.
Capabilities
With Elasticsearch, Aiden can:
- Fetch your Elasticsearch indices and their mappings
- Fetch and summarize targeted logs
- Perform log analytics
Custom Skills
On top of the several out-of-the-box capabilities, you can create custom skills to add additional capabilities.
See the Skills page for more information.
Example Interactions
- Fetch all the error-level logs in the past 2 hours
- Can you tell me how many warn-level logs were found on 9th May?
- Summarize any errors from the logs of the vm-agent pod present in the observe namespace
Configuration Steps
Create your Elasticsearch API Token
Use the curl command given below to generate the API key required for integration.
curl -k -u "<es_username>:<es_password>" -X POST "https://<your_es_url>/_security/api_key" -H "Content-Type: application/json" -d'
{
  "name": "opsverse-aiden-es-key",
  "role_descriptors": {
    "all_access": {
      "cluster": ["all"],
      "index": [
        {
          "names": ["*"],
          "privileges": ["all"]
        }
      ]
    }
  }
}'
The response to the above command will be in the following format.
{
   "id":"this_is_a_dummy_id",
   "name":"opsverse-aiden-es-key",
   "api_key":"<generated_api_key>",
   "encoded":"<base64_endcode_key>"
}
Make sure to use the base 64 encoded api key while configuring the integration
Configure the Integration in Aiden
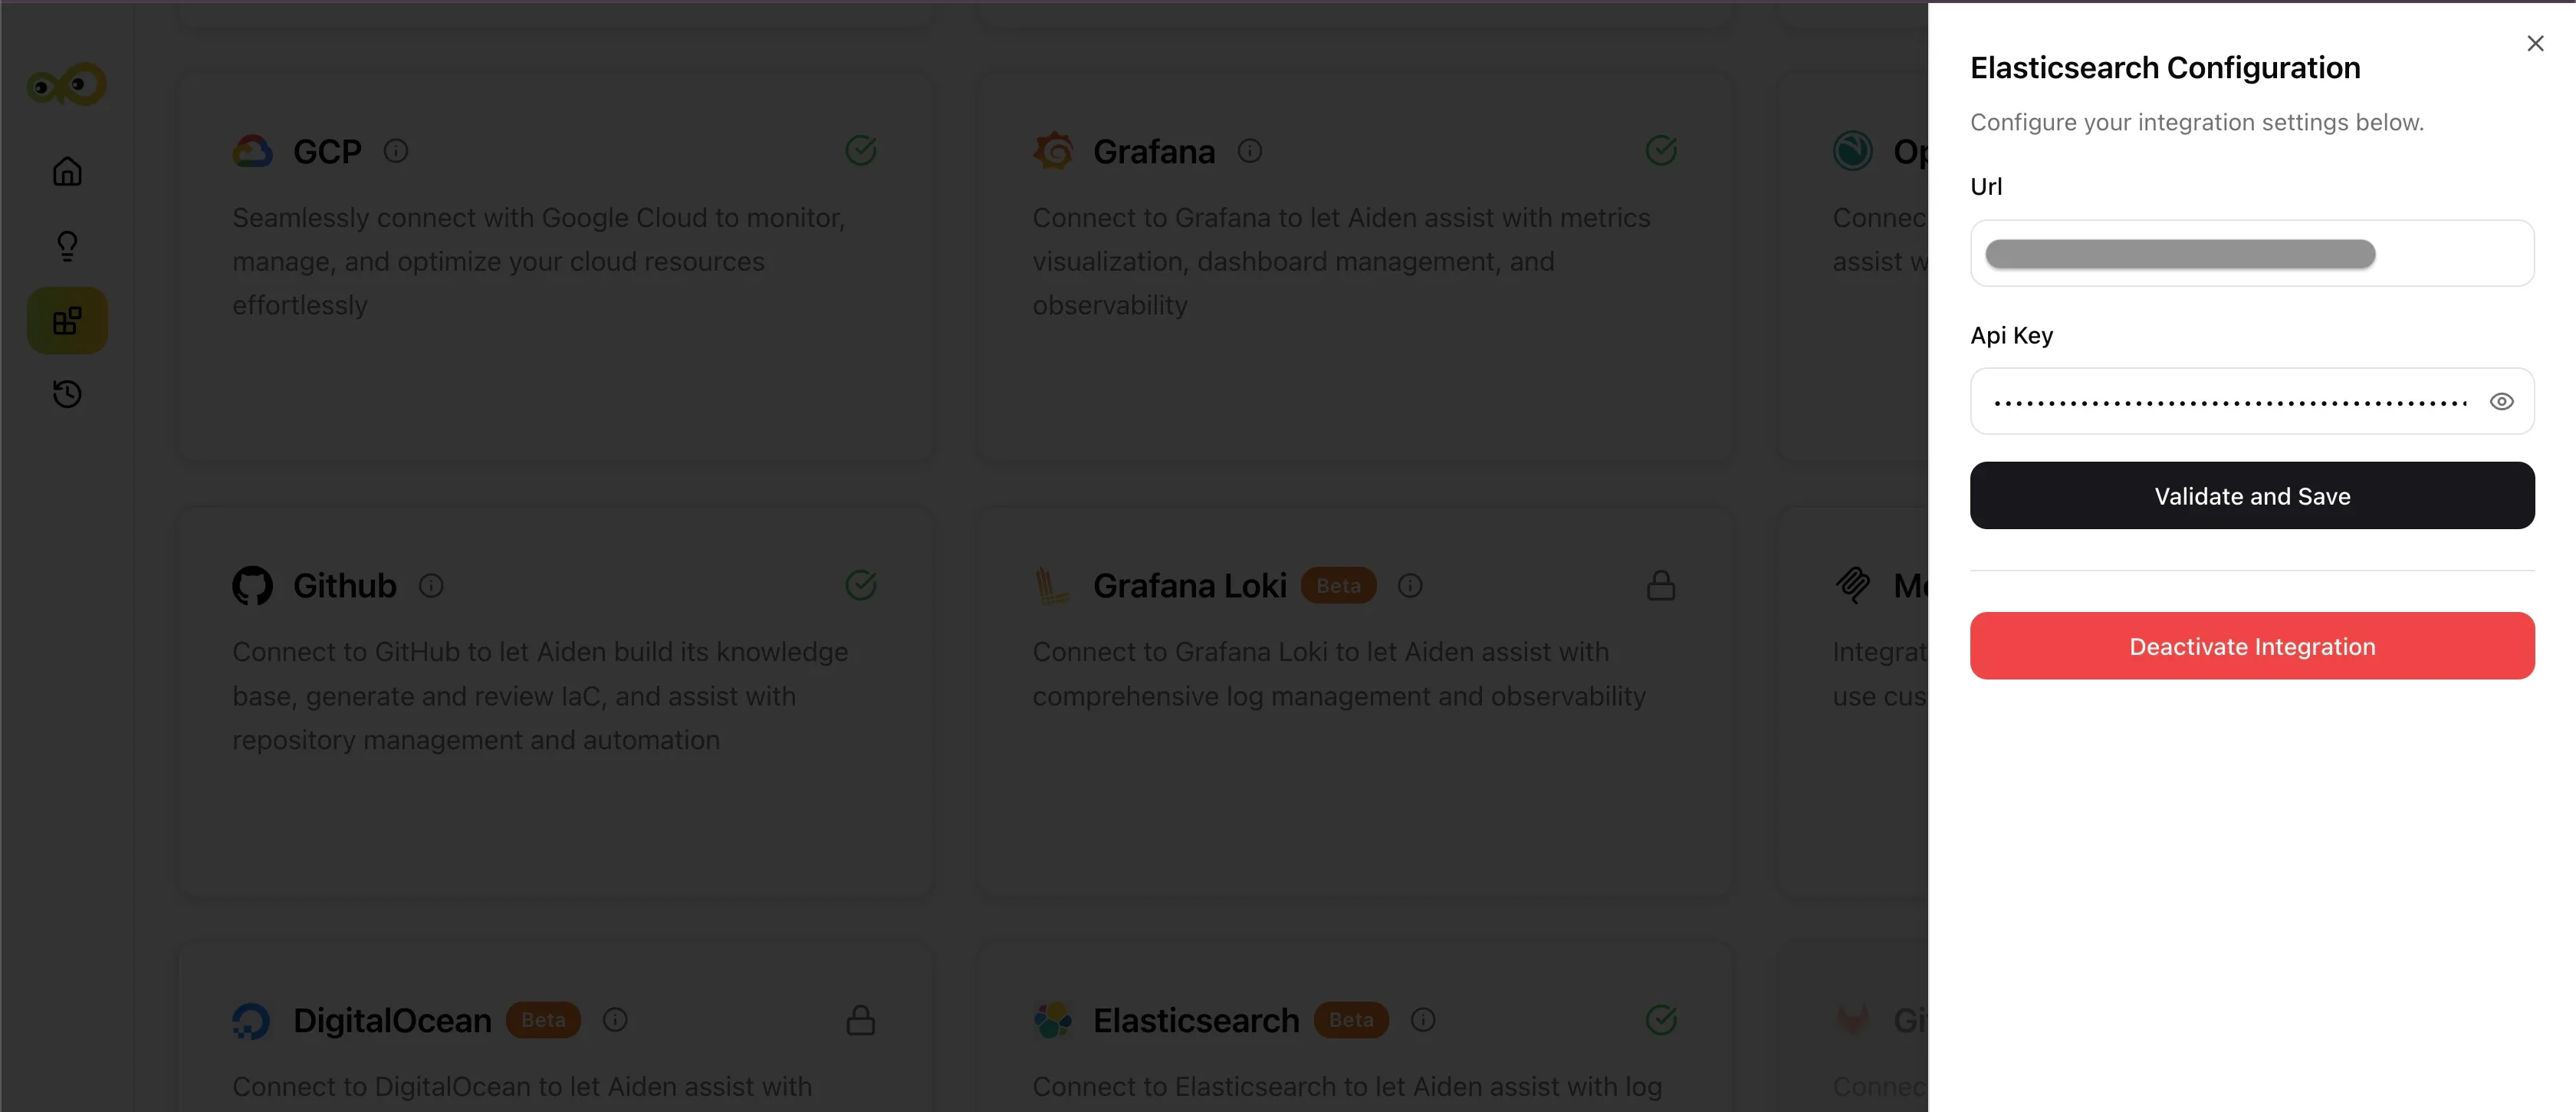
- Locate the Elasticsearch integration card and click Activate
- Configure your Elasticsearch credentials - URL: your Elasticsearch URL - API Token: base64 encode api token
- Click Save to enable the integration
Note: Ensure your Elasticsearch endpoint is accessible from Aiden's network