Cloudflare
Logs
ObserveNow can be used as a destination for Cloudflare CDN and worker log monitoring using Logpush.
Cloudflare's Logpush Custom HTTPS endpoint feature allows you to stream logs directly to ObserveNow. Logpush transmits logs in real-time batches without minimum size requirements.
Setup via Cloudflare Dashboard
- In the Cloudflare Dashboard, navigate to Analytics and Logs -> Logpush -> Create a Logpush job
- Navigate to Select a destination and choose HTTP destination.
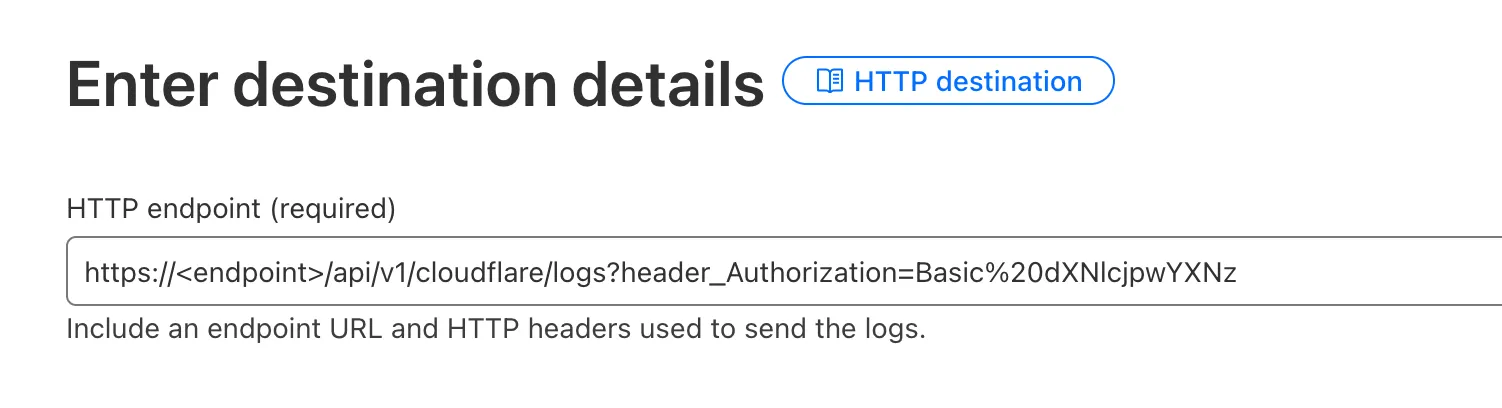
- Input the HTTP endpoint using your ObserveNow endpoint details, then click Continue. The format of the endpoint use will be https://<endpoint>/api/v1/cloudflare/logs?header_Authorization=Basic%20<base64(username:password)>
- Choose which dataset you want to forward to the destination service.
- Configure your logpush job settings:
- Set the Job name to observenow.
- Under If logs match, define filtering criteria to include or exclude specific events from your log stream. You can additionally filter in the ObserveNow console as well (described below)
- In Send the following fields, decide whether to transmit all available log data to ObserveNow or select specific fields only.
- Navigate to Advanced Options:
- Set timestamp field format to UnixNano for proper time handling.
- Click Submit to finalize your logpush job configuration.
Additional Filtering
In the OpsVerse Console, in ObserveNow configuration, under Integrations you should see Log Ingestion Settings. Click on Configure to filter Cloudflare logs matching different conditions. eg. filter out all access logs or only keep auth logs or logs containing specific words.
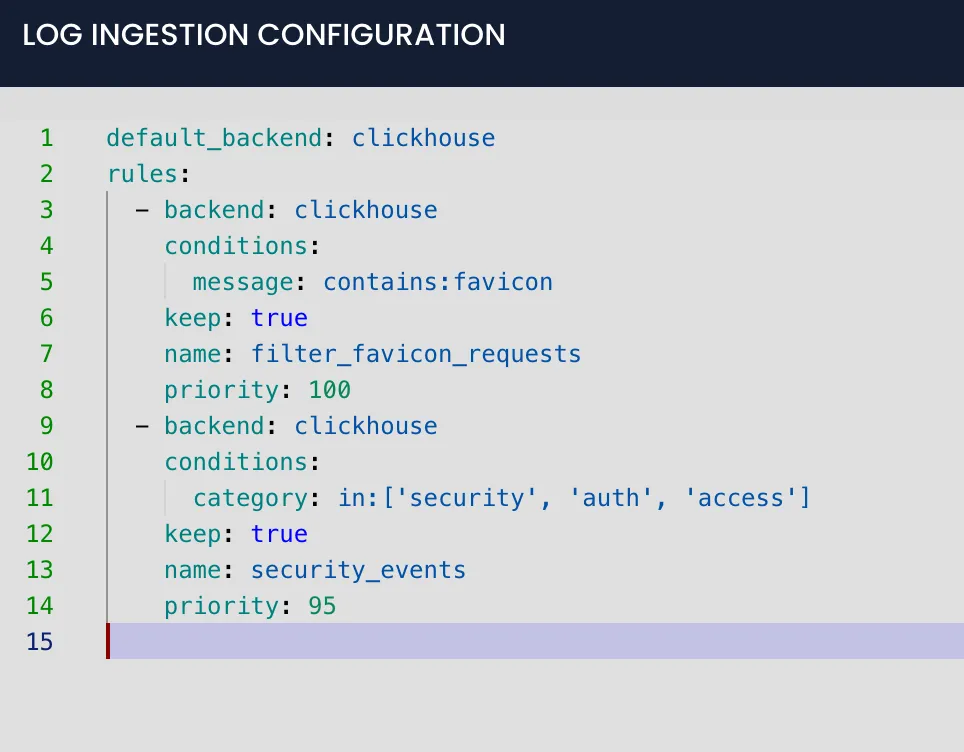
When filtering, you can use the priority to determine the priority of different filtering rules when processing logs
Metrics
OpsVerse's Kubernetes agent can be used to collect metrics from Cloudflare
For accessing Cloudflare metrics, create a Custom Token in Cloudflare withthe following permissions as described here: Account.Account Analytics:Read Account.Account Settings:Read Account.Account Rulesets:Read Zone.Firewall Services:Read and Zone.Analytics:Read
Add the following YAML snippets to the agent's values.yaml and run the agent based on these instructions.
cloudflare-exporter:
  enabled: true
  env:
    - name: CF_API_TOKEN:
      value: <CF_API_TOKEN>
    # Optional Configs
    - name: CF_ZONES
      value: zone1,zone2,zone3
  # Alternatively, add the above configurations into a secret and use
  # secretRef: <secretName>
Additional environment variables can be configured as descibed here
These metrics can be visualized using ready-to-use Grafana dashboards